Infrastructure
How our infrastructure works
Where our servers are, how traffic is filtered and what hardware runs your services. Explained simply, with technical details for those who want them.
A packet's journey
Every request to your service goes through these steps, whatever the plan.
01
Internet
Traffic comes in, legitimate or not.
02
IP Transit
First layer: Gcore, Netrix and EASIO-COM, our three IP transit providers, scrub the traffic and absorb volumetric attacks upstream.
03
VexCloud XDP filter
Second layer: suspicious packets are dropped in the Linux kernel.
04
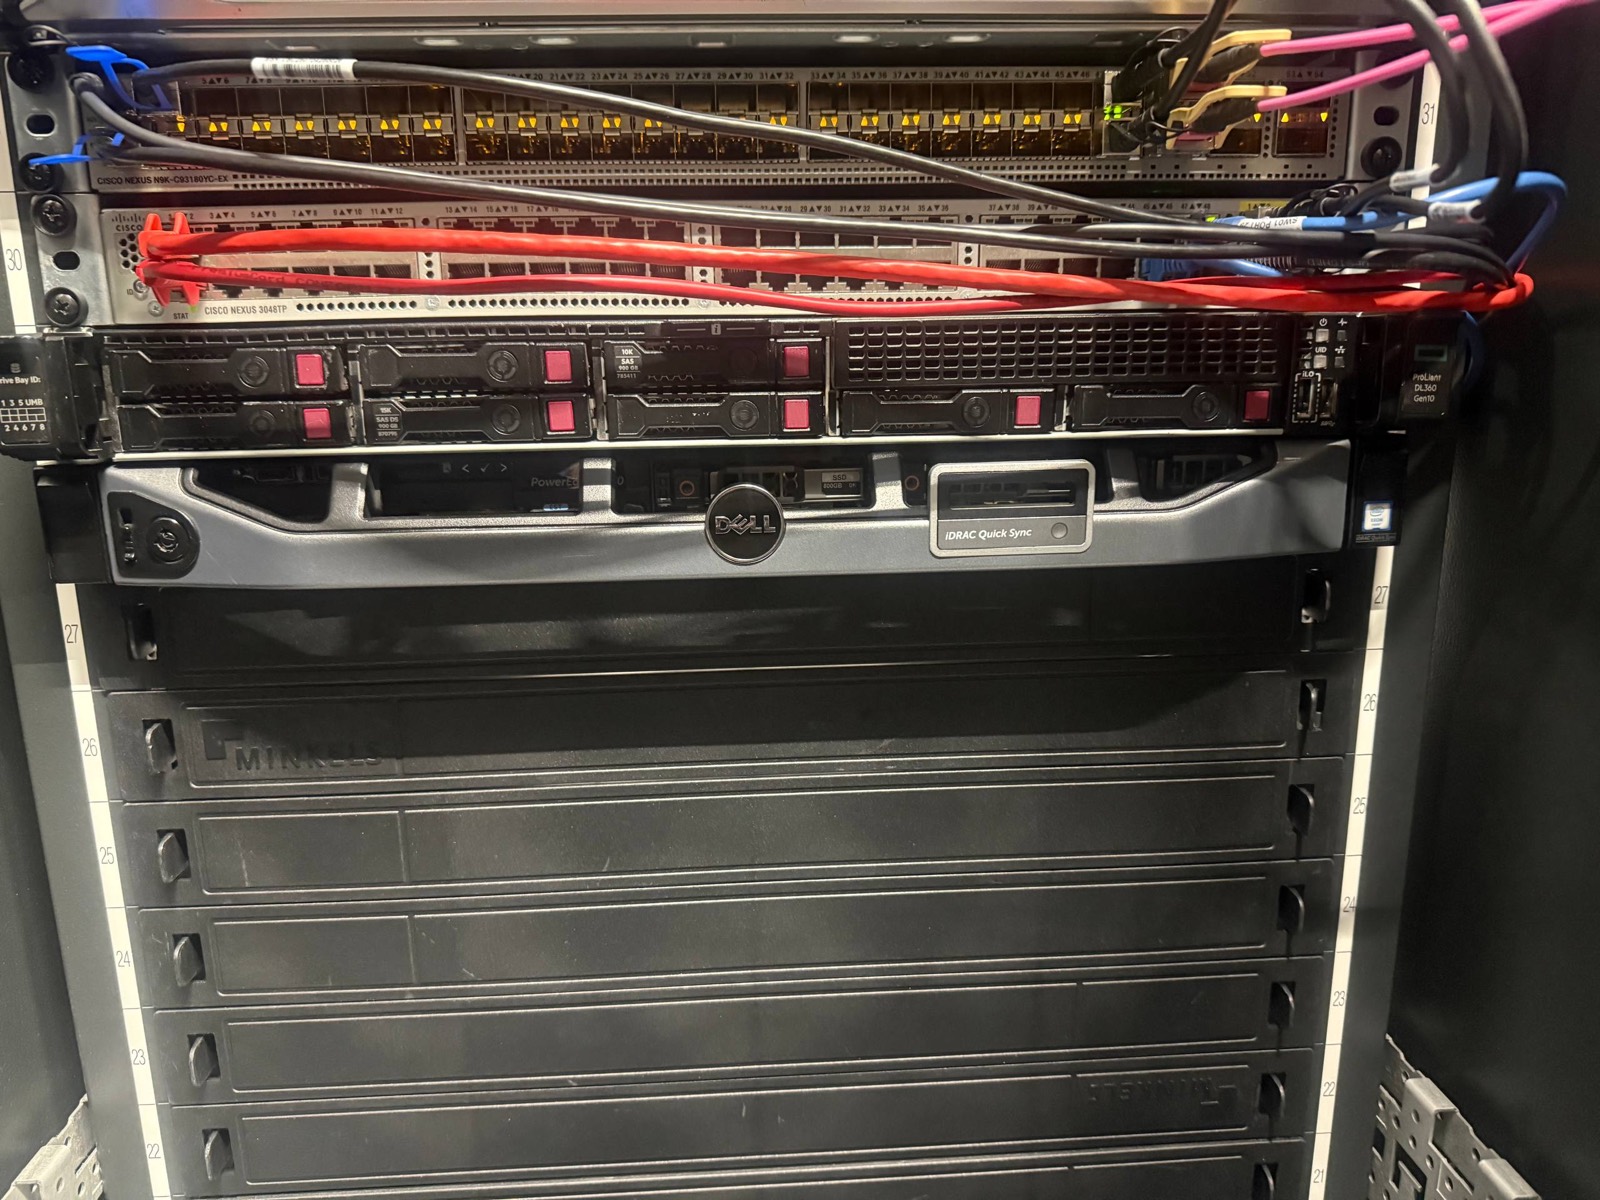
Equinix PA6, Paris
Our routers, connected over BGP to our three IP transit providers, active in parallel.
05
Your service
Your VPS, website or game server receives clean traffic.
Equinix PA6, Paris
- In plain words
- Our servers are installed in an Equinix data center in Paris, built to run network and IT equipment around the clock.
- Technical side
- Rack hosting at Equinix PA6. Close to Paris internet exchanges, low latency to France and Western Europe.
Three IP transit providers
- In plain words
- Our network connects to the Internet through three IP transit providers at once. If one has a problem, the others keep carrying traffic.
- Technical side
- BGP sessions with Gcore IP Transit, Netrix IP Transit and EASIO-COM IP Transit, active in parallel.
DDoS filtering, layer 1
- In plain words
- Large attacks are absorbed before they even reach us, by the networks of our three IP transit providers.
- Technical side
- Gcore, Netrix and EASIO-COM: upstream scrubbing of volumetric traffic on each of the three transits.
DDoS filtering, layer 2
- In plain words
- What remains is sorted directly by our servers' system, very early and very fast.
- Technical side
- In-house XDP program running in the Linux kernel, before the network stack: UDP/TCP floods dropped as early as possible.
DDoS panel
Your DDoS protection, tuned by you
Every IP address is configured from the VexCloud DDoS panel: filtering mode, allowed ports, blocklist and alerts. Changes apply directly to the XDP filter.
Six filtering modes
Full, TCP only, UDP only, Open, Closed or Bypass: choose what gets filtered, one IP address at a time.
Rules and ports
Ready-made filters for SSH, HTTP/HTTPS, RDP, FiveM, Steam, Minecraft, WireGuard… and up to 32 custom ports or ranges per IP.
Blocklist and allowlist
Block or allow an IP or a CIDR range, temporarily or permanently. Deny a whole protocol: TCP, UDP or ICMP.
Packet threshold
A packets-per-second cap per IP, from 50,000 to 500,000, to drop the excess as early as possible.
Attack history
Every attack with its type, peak and duration, plus traffic origins by country and network (ASN).
Alerts and API
Discord or custom API webhooks when an attack starts and ends, browser notifications and a documented API.
Available from your client area, with VPS, dedicated servers, IP tunnels and VPS reseller plans.
The hardware behind each service
| Service | Processor | Storage | Network |
|---|---|---|---|
| VPS | Intel Xeon Gold 6138 | NVMe | Node connected at 50 Gbit/s |
| VPS reseller | Intel Xeon E5-2680 v4 | NVMe | Node connected at 50 Gbit/s |
| Pterodactyl reseller | Intel Xeon Gold 6138 | NVMe | Node connected at 50 Gbit/s |
Transparency on availability
The state of our services and ongoing incidents are published in real time on our public status page.